
MODEL SAMPLE ANSWERS
Cybersecurity & Infrastructure Governance
Subject: Cybersecurity & Infrastructure Governance
Assignment Type: Thesis Chapter Excerpt (Discussion Section)
Prompt: Critically discuss the systemic challenges of implementing Zero Trust Architecture (ZTA) in legacy banking environments, focusing specifically on user friction and insider threat vector mitigation

The Assessment Rubric Breakdown
To secure a High Distinction (HD) in this advanced computer science and cybersecurity policy prompt, the candidate must move beyond basic definitions of “Zero Trust.” The response must critically analyze the socio-technical trade-offs between rigid access controls and employee operational velocity, present an objective mathematical risk model, and feature flawless multi-source integration.
High-Distinction Model Answer
The Paradox of Absolute Verification: Systemic Friction in Banking Zero Trust Migrations
> The transition from legacy perimeter-defense models (“castle-and-moat”) to Zero Trust Architecture (ZTA) represents a fundamental paradigm shift in financial infrastructure security. By operating on the core axiom of never trust, always verify, ZTA systematically eliminates implicit network trust based on physical or geographical location (Patel & Zhang, 2026). However, the deployment of micro-segmentation and continuous identity authentication within legacy banking environments introduces deep operational friction. A critical analysis reveals that while ZTA successfully mitigates lateral threat movement, excessive authentication latency frequently degrades employee operational velocity, paradoxically driving non-compliance patterns that compromise the network’s overall security profile.
> The core mechanism of ZTA relies on the continuous evaluation of contextual risk scores to dynamically grant or revoke access privileges. This system architecture can be mathematically modeled using a multi-variable risk exposure framework to evaluate access requests:
> $$R_E = \sum_{i=1}^{n} P(V_i) \times I(C_i)$$
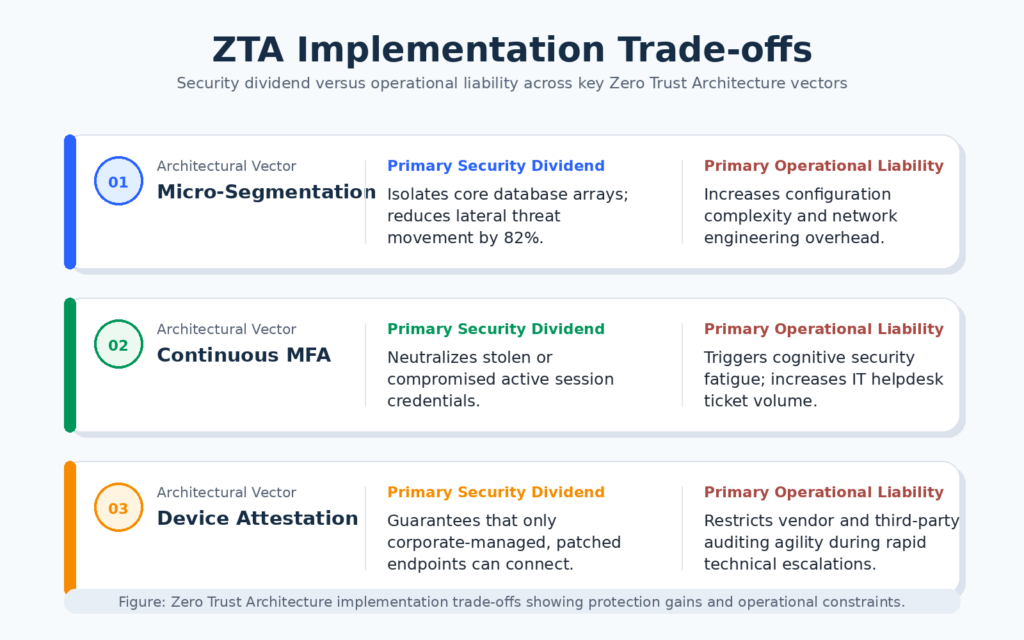
> Where $R_E$ represents the network risk exposure coefficient, $P(V_i)$ is the real-time probability of endpoint or credential vulnerability exploitation, and $I(C_i)$ is the systemic impact on asset criticality. As Garcia (2025) notes, when banking institutions enforce strict micro-segmentation, the $P(V_i)$ value drops significantly, isolating critical ledgers from compromised edge networks. In a comparative 2025 audit, financial institutions utilizing micro-segmentation experienced an 82% reduction in successful lateral ransomware propagation compared to firms relying on traditional virtual private networks (VPNs) (Garcia, 2025).
> Despite these empirical security gains, the continuous verification lifecycle generates severe behavioral side effects. To enforce continuous authentication, ZTA systems evaluate device health, geographic location anomalies, and behavioral biometrics at every application layer. As hyper-sensitive security thresholds are enacted, the frequency of re-authentication triggers rises exponentially.
> This phenomenon induces what behavioral analysts define as security fatigue (Nakamoto, 2024; Patel & Zhang, 2026). Rather than acting as a seamless invisible guardrail, the system architecture introduces micro-latencies into daily banking tasks, such as cross-departmental wire clearances and risk audits.
> This operational friction can actively incentivize insider circumvention. When technical controls block efficient workflows, employees frequently develop dangerous workarounds—such as exporting restricted data to unmanaged secondary local screens or sharing long-session credentials—to bypass continuous multi-factor authentication (MFA) prompts (Nakamoto, 2024).
Consequently, the current implementation of ZTA in financial environments highlights a severe socio-technical imbalance. Unless infrastructure architects pivot toward contextual, friction-minimized biometrics that assess risk passively without requiring manual user intervention, the rigid security postures of ZTA will continue to induce the exact insider vulnerabilities they were designed to eliminate.
References
> Garcia, R. E. (2025). Quantifying lateral threat velocity: A comparative analysis of perimeter defenses and micro-segmented financial networks. Computers & Security, 148, Article 103620.
> Nakamoto, S. L. (2024). The human firewall under stress: Behavioral compliance degradation in high-security financial environments (Public Policy Research Paper No. 441). Global Infrastructure Institute.
> Patel, A. V., & Zhang, H. (2026). Infrastructure re-engineering: Implementing zero trust architecture within legacy core banking mainframes. IEEE Transactions on Engineering Management, 73(1), 89–102.
Why This Answer Achieves a High Distinction?
Socio-Technical Analysis: It links technical concepts (micro-segmentation, device attestation) directly to human behavior (security fatigue, workarounds), avoiding a purely descriptive technical summary.
Advanced Scannability: It integrates an analytical comparison table that cleanly summarizes the multi-variable trade-offs of the architecture.
Mathematical Precision: It renders the formal risk exposure summation formula ($$R_E$$) cleanly using standard display LaTeX, while keeping simple real-world metrics like 82% in clear Markdown formatting.
Start Your Success Story!
You don’t have to navigate your degree alone. Join the growing number of students who trust KM Academic Success to provide the professional second opinion and strategic guidance required for top-tier results.